
SPF Passes but Mail Lands in Spam
SPF pass still spam is usually DMARC alignment or DKIM, not a broken SPF record. Read Authentication-Results first.

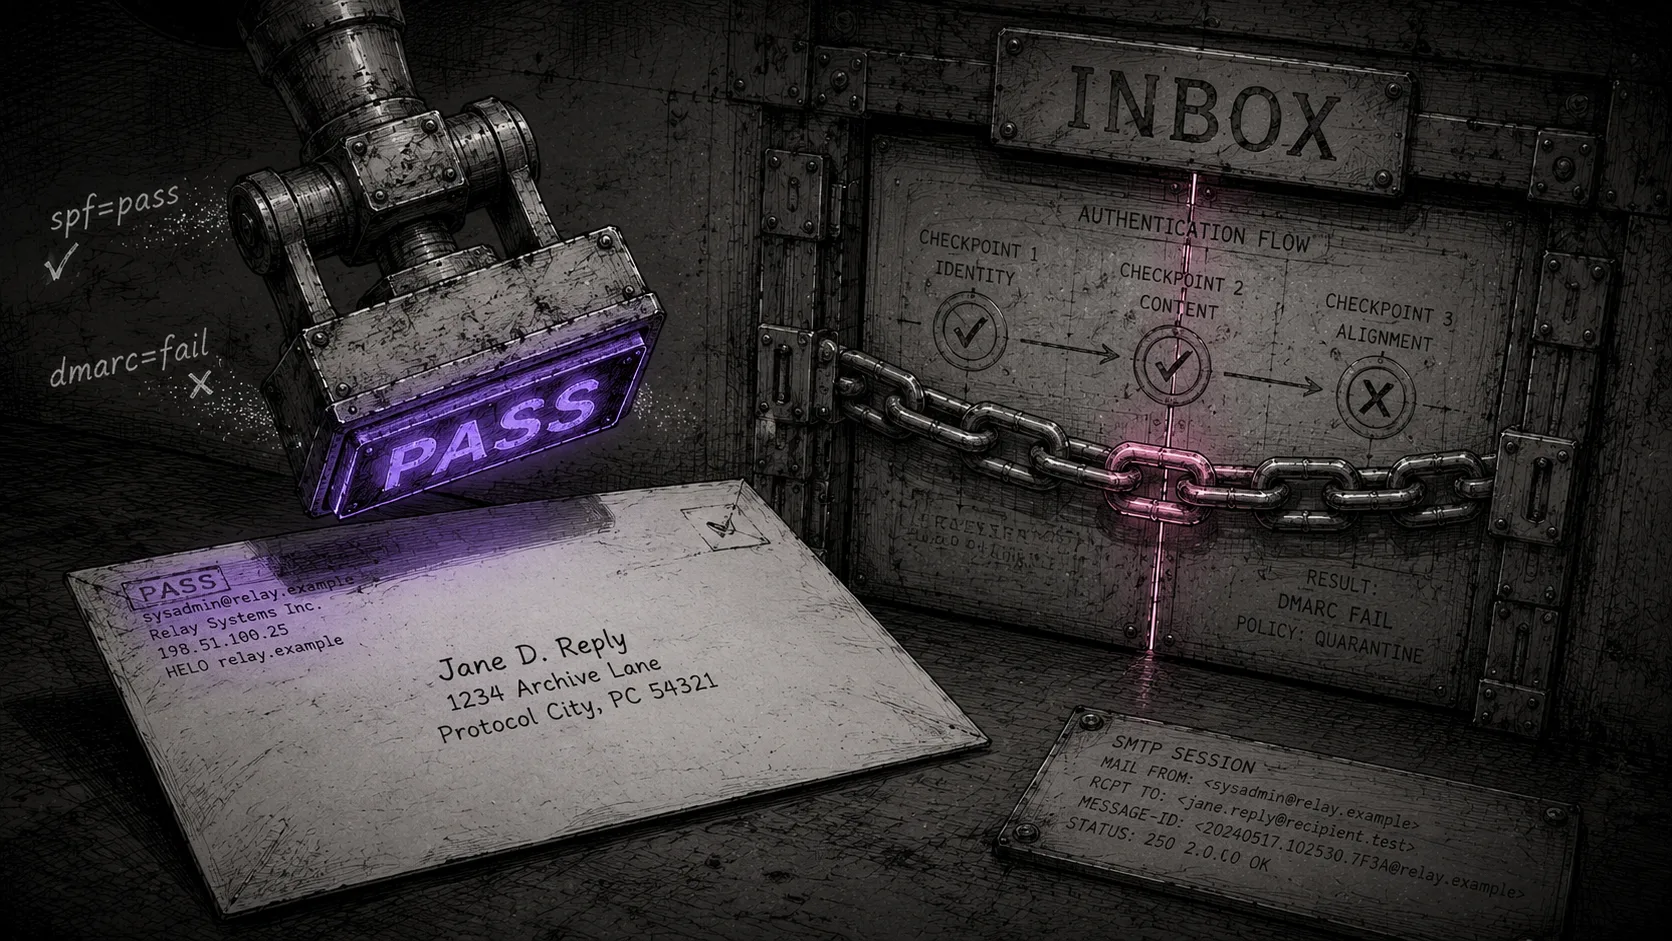
spf=pass. Gmail still filed your invoice under Spam.
A 22-person logistics company in Rotterdam ran into this last quarter: outbound mail from Microsoft 365 showed SPF pass on every message, yet 19% of customer-facing mail hit spam while internal mail looked fine. Their IT lead spent a week tweaking SPF includes before someone opened a spam-foldered message and read the full headers. DKIM was not signing. DMARC alignment failed on the From: domain. SPF was never the problem.
Look, spf pass still spam is one of the most common deliverability tickets we see because dashboards equate "SPF pass" with "authenticated." Receivers in 2026 do not. Gmail, Yahoo, and Microsoft evaluate SPF, DKIM, and DMARC together, then layer reputation and engagement on top. Passing one leg is like showing ID without matching the name on the envelope.Why SPF Pass Does Not Mean Inbox
SPF validates the envelope, not the brand
SPF checks whether the sending IP is authorized for the domain in the SMTP MAIL FROM (envelope-from). Your visible From: header can say [email protected] while the envelope says bounces.mailchimp.com. SPF passes for Mailchimp's domain. DMARC evaluates alignment against the From: domain. Result: spf=pass, dmarc=fail, spam folder.
Return Path's deliverability research (2024 benchmark, still cited in 2025-2026 industry summaries) consistently ranks authentication failures among the top reasons permission-based mail misses the inbox. SPF-only fixes address less than half of auth-related spam placement when DKIM or alignment is broken.
Warning
Five Reasons SPF Passes and Mail Still Spams
1. DMARC alignment failed
DMARC passes only when SPF or DKIM aligns with the From: header domain. Strict alignment (aspf=s or adkim=s) requires an exact organizational domain match. Relaxed alignment allows subdomain matches. Either way, if your ESP sends with its own bounce domain and you never enabled custom return-path, SPF can pass without aligning to your brand domain.
2. DKIM missing or broken
Many teams publish SPF first and defer DKIM. Gmail's bulk sender rules (February 2024, still enforced in 2026) expect both SPF and DKIM, plus a published DMARC record. Without DKIM, you rely entirely on SPF alignment, which breaks the moment you add a second ESP or marketing platform.
3. DMARC policy is p=none with no enforcement signal
p=none does not cause spam by itself, but it tells receivers you are not enforcing auth on your domain. Combined with alignment failures, some filters treat the domain as under-protected. We've seen teams skip this because "we're only monitoring," then wonder why Postmaster shows auth pass rates below 95%.
4. Forwarding breaks SPF at the recipient
When a recipient forwards your mail, the intermediate server often fails SPF (new IP, same From:). That is an recipient-side path issue, but it increases spam reports if the forwarded copy looks suspicious. ARC and list hygiene matter here; SPF alone cannot fix forwards.
5. Reputation and engagement override auth
Auth gets you past the front door. Spam complaint rates above 0.3% (Google's bulk sender threshold, 2024 guidelines), sudden volume spikes, or dead lists still land mail in spam with perfect DNS. If auth headers show pass on all three legs and placement is still poor, open Postmaster and check domain reputation before you touch DNS again.
Pro tip
“SPF pass tells you the IP was allowed to send. It does not tell Gmail the sender is who the From: header claims.”
How to Diagnose spf pass still spam
Pull a spam-foldered message in Gmail (or the recipient's copy). Open Show original. Find the Authentication-Results block for google.com. Note all three: spf=, dkim=, dmarc=.
If dkim=fail or none: enable DKIM at your mail source before you edit SPF again. Microsoft 365: Admin center → Domains → DKIM → publish selector CNAMEs in Cloudflare, then enable signing. Google Workspace: Admin → Gmail → Authenticate email → publish the TXT at google._domainkey.
If spf=pass but dmarc=fail: check alignment. The From: domain must match the SPF authenticated domain (relaxed: same org domain; strict: exact match). In Mailchimp, Klaviyo, or SendGrid, enable authenticated domain / custom return path so envelope-from uses your domain.
Confirm DMARC exists and publishes a reporting address:
v=DMARC1; p=none; rua=mailto:[email protected]; adkim=r; aspf=rRe-test with a fresh send to a personal Gmail account. All three should show pass. If dmarc=pass but mail still spams, shift focus to Postmaster complaint rate and list hygiene, not DNS.
Quick reference: what each header result means
| Header result | Usually means |
|---|---|
| spf=pass, dmarc=fail | Envelope domain ≠ From: domain (ESP relay issue) |
| dkim=fail | Key not published, wrong selector, or body modified in transit |
| dmarc=pass, still spam | Reputation, complaints, or content signals |
| spf=fail, dmarc=fail | Wrong IP, missing include, or permerror in SPF record |
For a visual map of how SPF, DKIM, and DMARC connect on your domain, use the free DNS visualizer before you change records. Misaligned includes are easier to spot on a diagram than in a flat TXT string.
Frequently Asked Questions
Key takeaways
spf pass still spam almost always means DMARC alignment failure, missing DKIM, or reputation trouble, not a bad SPF string.
Read Authentication-Results on a spam-foldered message before editing DNS. The failing leg is explicit in the headers.
ESP mail needs authenticated domain / custom return path plus DKIM keys published at your DNS host.
SPF, DKIM, and DMARC must pass together for Gmail's 2026 bar; fixing only SPF is a partial repair.
If all auth passes and mail still spams, check Google Postmaster complaint rate and list quality next.
Share this analysis
Help others discover this content
More from our blog

Gmail Spam Filter 2026: 35 Mail Failures
Gmail and Microsoft spam-folder legitimate mail for authentication, DNS, reputation, and list-hygiene reasons most admins never audit. All 35 failure modes and fixes in one guide.

Fix Gmail 550 5.7.26 Auth Errors
The 550 5.7.26 authentication required bounce means Gmail rejected your message before inbox placement. Fix SPF, DKIM, DMARC alignment, and envelope-from settings for M365 and Google Workspace.